
 TixFin
API Authentication
Secure your API requests
Learn how to authenticate your Partner API requests securely.
Authentication Method
The Partner API uses API Keys in prefix.secret format, scoped per
project to one or more endpoint groups (events.read,
ticket_catalog.read, tickets.read, orders.read). A request succeeds only
when the key carries the endpoint's group and the project has that group
enabled, so switching a group off cuts every key off it without revoking
anything.
The prefix is public and identifies the key in logs and the access trail; the secret is stored only as a keyed hash and cannot be recovered.
Send the key as either header:
GET /api/partner/projects/{projectId}/events
Host: beta-rest-api.tixfin.com
X-API-Key: YOUR_API_KEY
or as a bearer token:
GET /api/partner/projects/{projectId}/events
Host: beta-rest-api.tixfin.com
Authorization: Bearer YOUR_API_KEYThere's no separate test/live mode for the Partner API — a key is scoped to exactly one project and only to the endpoint groups you grant it.
Getting Your API Key
- Log in to beta.tixfin.com with two-factor authentication
- Select the project, then open the account menu → Account → Integrations (under Billing)
- Enable the Endpoint groups this project should expose
- Click Create API key and enter a Key name
- Choose the Allowed endpoint groups
- Copy the Raw API key and save it securely (shown once!)
You need access to the project's settings. Every change on this page asks for your second factor if you have not confirmed it in the last ten minutes.
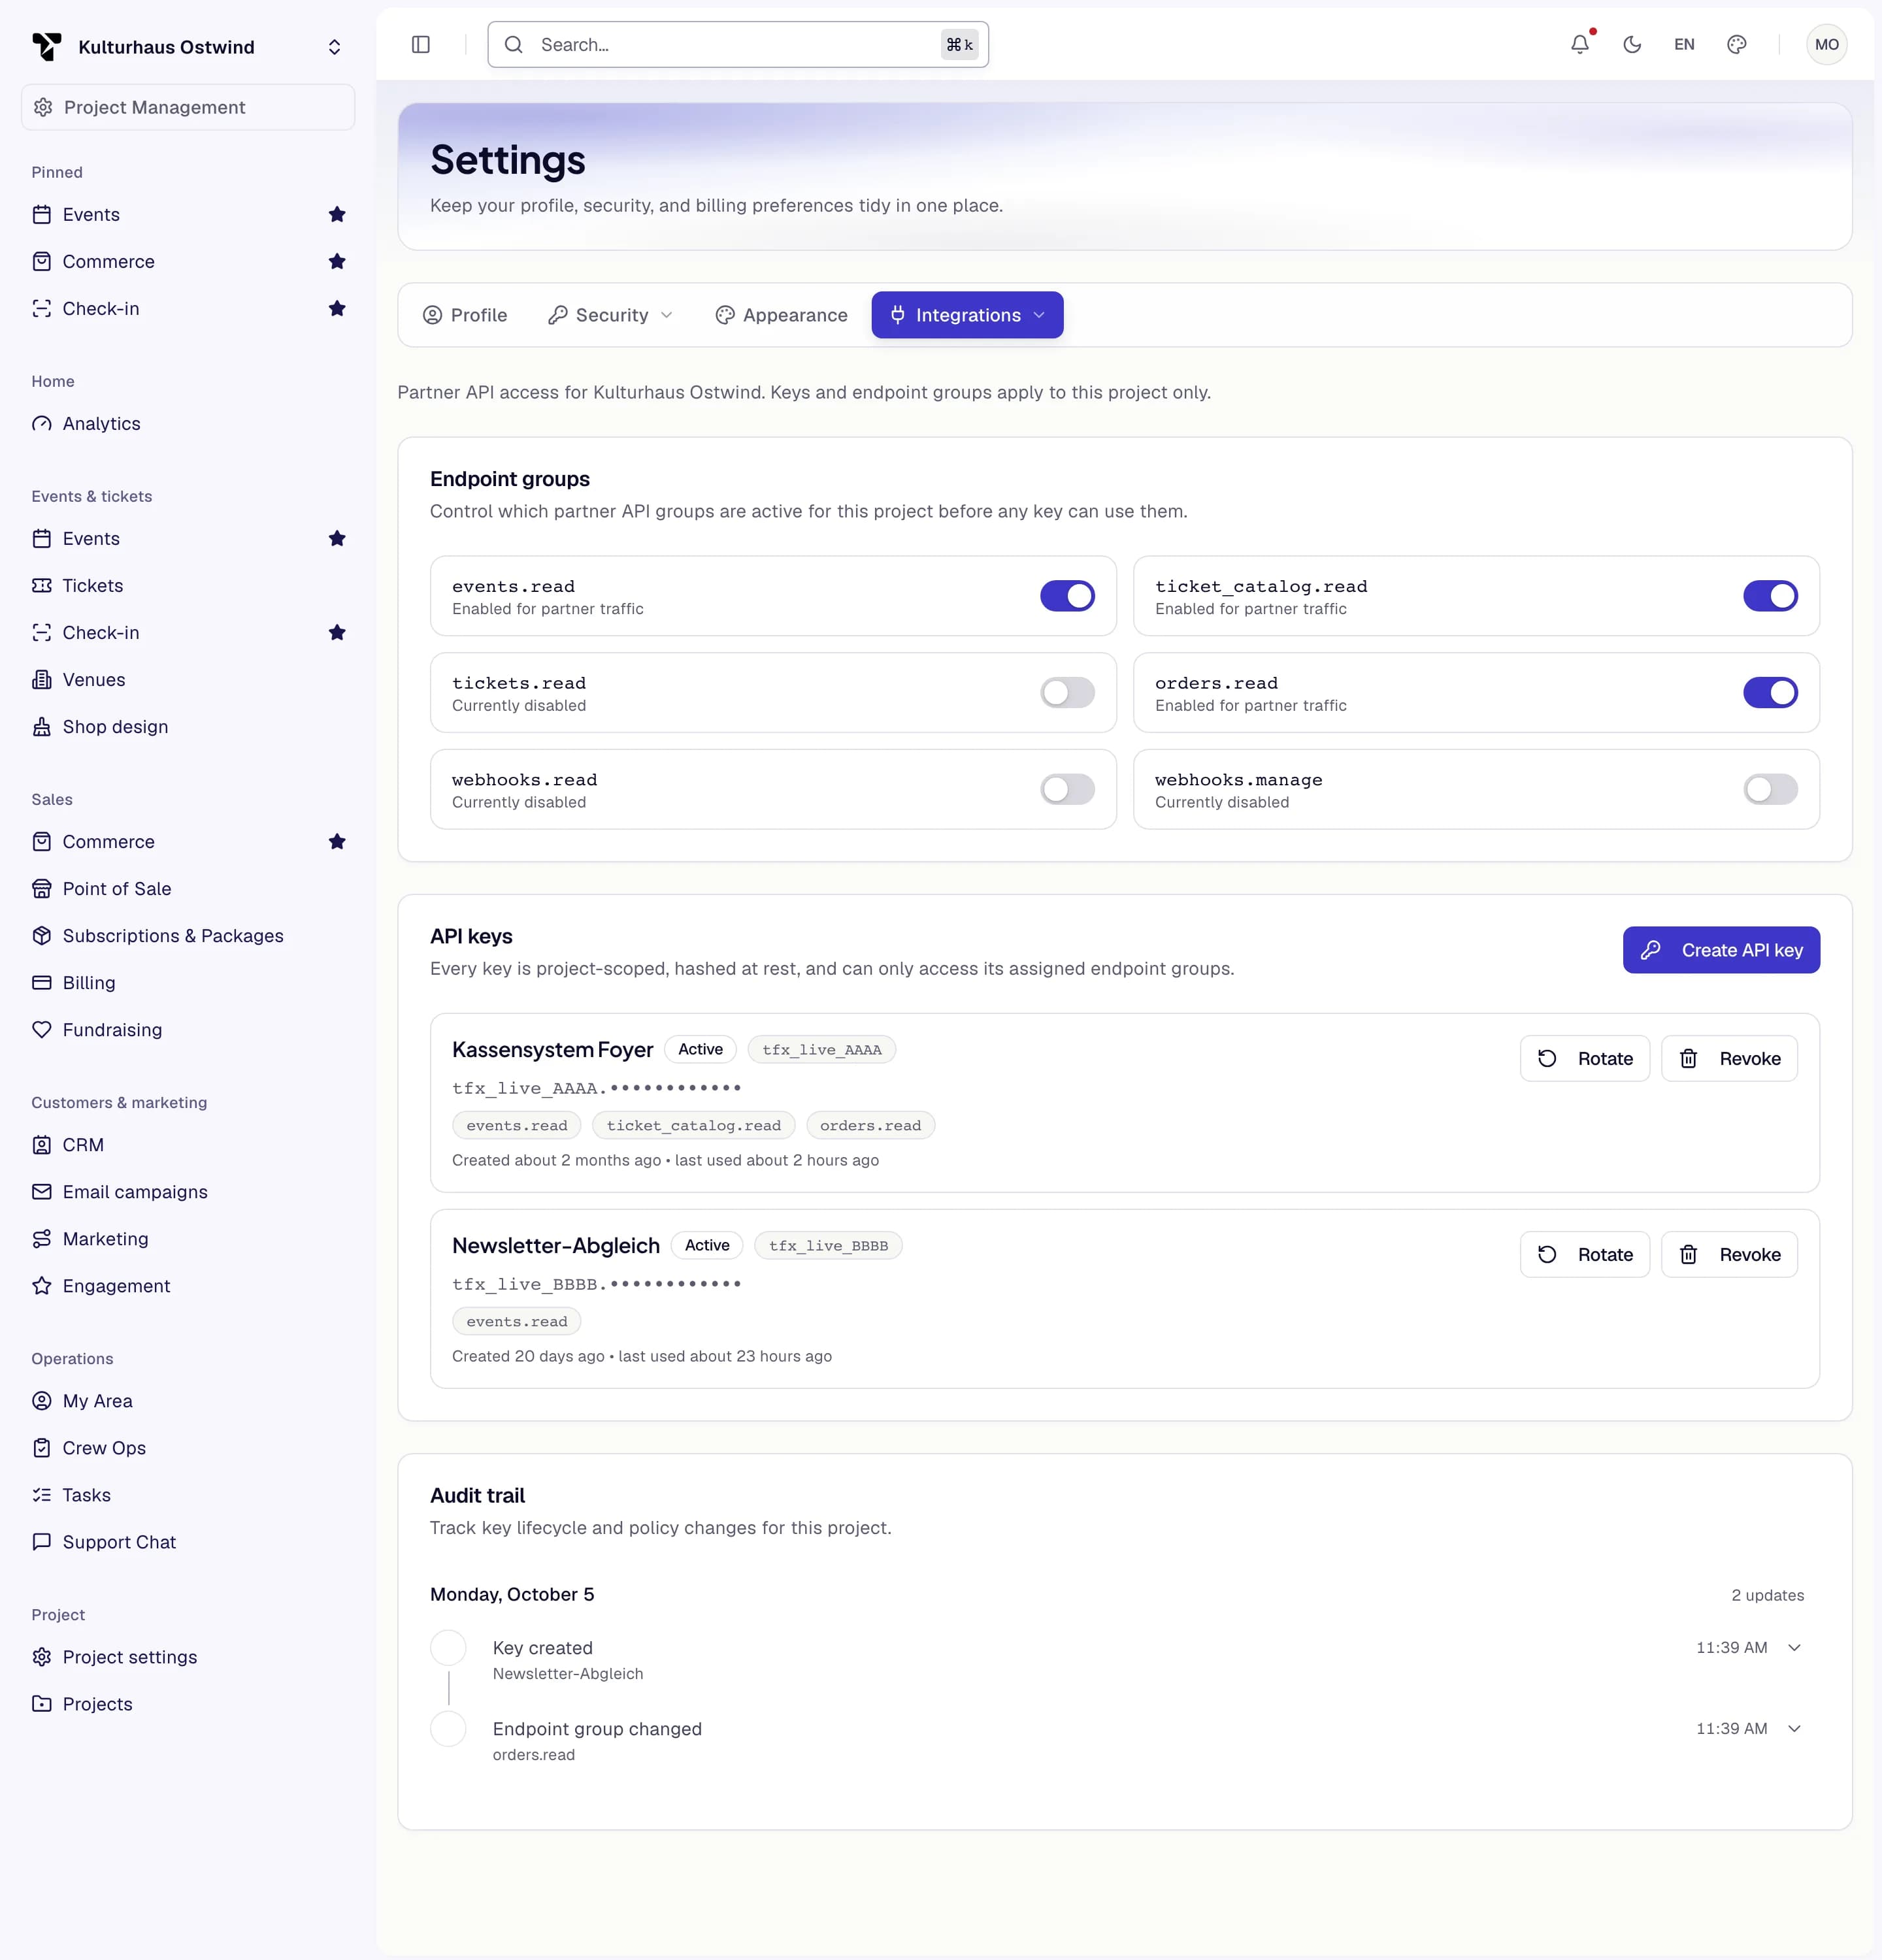
- Integrations
- Endpoint groups
- Create API key
- Rotate or revoke a key
Code Examples
npm install @tixfin/partner-api-clientimport { TixfinPartnerClient } from "@tixfin/partner-api-client";
const client = new TixfinPartnerClient({
projectId: process.env.TIXFIN_PROJECT_ID,
apiKey: process.env.TIXFIN_PARTNER_API_KEY,
baseUrl: "https://beta-rest-api.tixfin.com",
});
const events = await client.listEvents();
console.log(events.items);pip install tixfin-partner-apiimport os
from tixfin_partner_api import TixfinPartnerClient
client = TixfinPartnerClient(
project_id=os.environ["TIXFIN_PROJECT_ID"],
api_key=os.environ["TIXFIN_PARTNER_API_KEY"],
base_url="https://beta-rest-api.tixfin.com",
)
events = client.list_events()
print(events.items)curl "https://beta-rest-api.tixfin.com/api/partner/projects/$TIXFIN_PROJECT_ID/events" \
-H "X-API-Key: $TIXFIN_PARTNER_API_KEY"See the SDKs guide for the full client reference, or call the REST API directly with any HTTP client.
Error Handling
Common Authentication Errors
| Code | detail | Solution |
|---|---|---|
| 401 | An API key is required. | Add the X-API-Key or Authorization: Bearer header |
| 401 | Invalid API key. | The key is malformed, revoked, rotated, expired or never existed. The response does not say which |
| 403 | This API key is not issued for that project. | Call the projectId the key was created for |
| 403 | This API key does not carry the … endpoint group. | Create or use a key with that group |
| 403 | The … endpoint group is disabled for this project. | Enable the group under Endpoint groups |
| 429 | Partner API rate limit exceeded. / API key rate limit exceeded. | Wait for the Retry-After seconds (see limits below) |
Error Response
{
  "title": "Unauthorized",
  "status": 401,
  "detail": "Invalid API key.",
  "timestamp": "2026-10-25T09:30:00.000000000Z"
}
Security Best Practices
✅ Do This
Store Securely
# Environment variables (recommended)
export TIXFIN_PARTNER_API_KEY="YOUR_API_KEY"
Scope Narrowly
- Only grant the endpoint groups (
events.read,tickets.read, etc.) a key actually needs - Create separate keys per integration instead of sharing one broadly
Rotate Regularly
- Rotate keys periodically from Account → Integrations. Rotation keeps the key's name and groups and issues a new prefix and secret; the old key stops working at once
- Revoke keys you no longer use
Use HTTPS Only
- Never send keys over HTTP
- Always use
https://beta-rest-api.tixfin.com
❌ Don't Do This
Never commit to Git
// ❌ BAD
const apiKey = "YOUR_API_KEY";

// ✅ GOOD
const apiKey = process.env.TIXFIN_PARTNER_API_KEY;
Never use client-side
<!-- ❌ BAD - API key exposed to users -->
<script>
  const apiKey = "YOUR_API_KEY";
</script>
The Partner API is read-only, but a leaked key still exposes your event, ticket, and order data — treat it like any other secret.
Rate Limits
| Scope | Sustained rate | Burst |
|---|---|---|
| Per API key | 10 requests/second (600/minute) | 60 |
| Per IP address | 5 requests/second (300/minute) | 30 |
Exceeding either returns 429 with a Retry-After header in seconds.
Need Help?
Can't authenticate?
- Check the key is correct (copy-paste fresh, no surrounding whitespace)
- Confirm you're calling the right
projectId - Verify the key hasn't been revoked or rotated
- Check the key is scoped for the endpoint group you're calling, and that the group is enabled for the project
Still stuck?
- Email: api@tixfin.com
- Include: your key's prefix only (never the full key), the endpoint you called, the error message